

















Behavior-based detection
Real-time process analysis blocks new threats with no prior knowledge of the code.
SentinelOne provides autonomous protection for endpoints, servers, identities and cloud environments. It analyzes process behavior in real time and detects, blocks and investigates unusual threats and Zero Day attacks, without relying on prior signatures. The platform includes identity monitoring, AI governance enforcement and incident management.
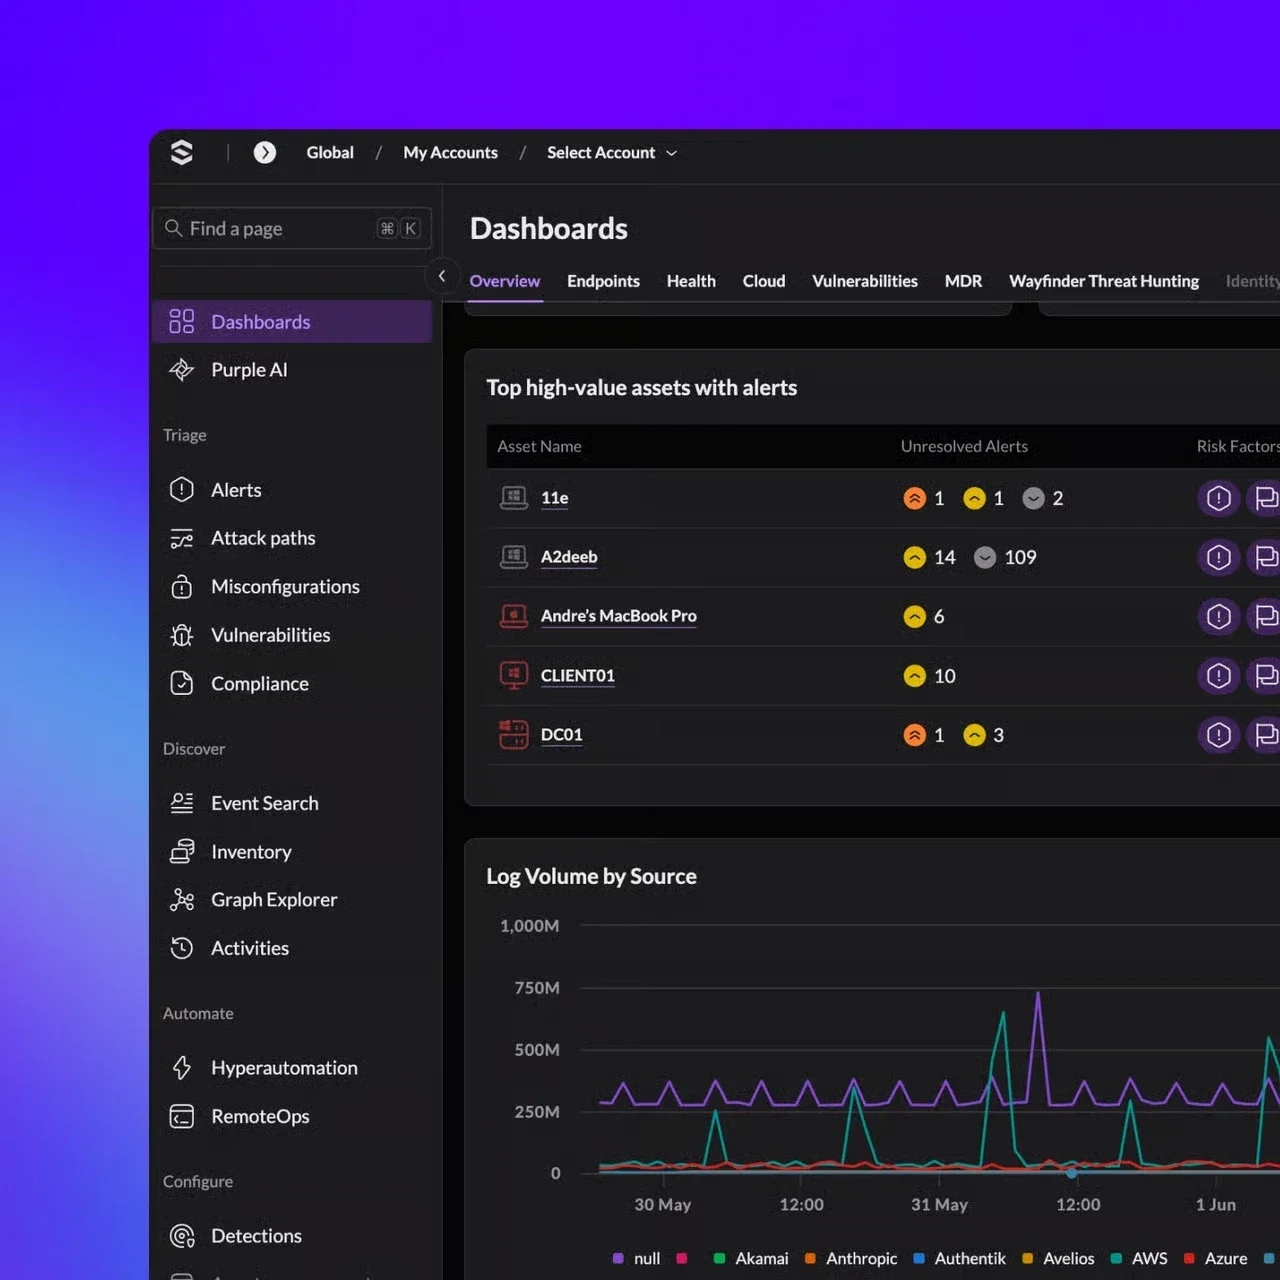
One dashboard for triage, discovery and automation: alerts, attack paths, misconfigurations, vulnerabilities, event search, Purple AI and Hyperautomation.
Real-time process analysis blocks new threats with no prior knowledge of the code.
Securing Active Directory and Entra ID infrastructure and disrupting attacks with deception mechanisms.
An MDR service with SOC experts and AI for monitoring and threat hunting.
Visibility and policy enforcement over GenAI application use, preventing data leakage.
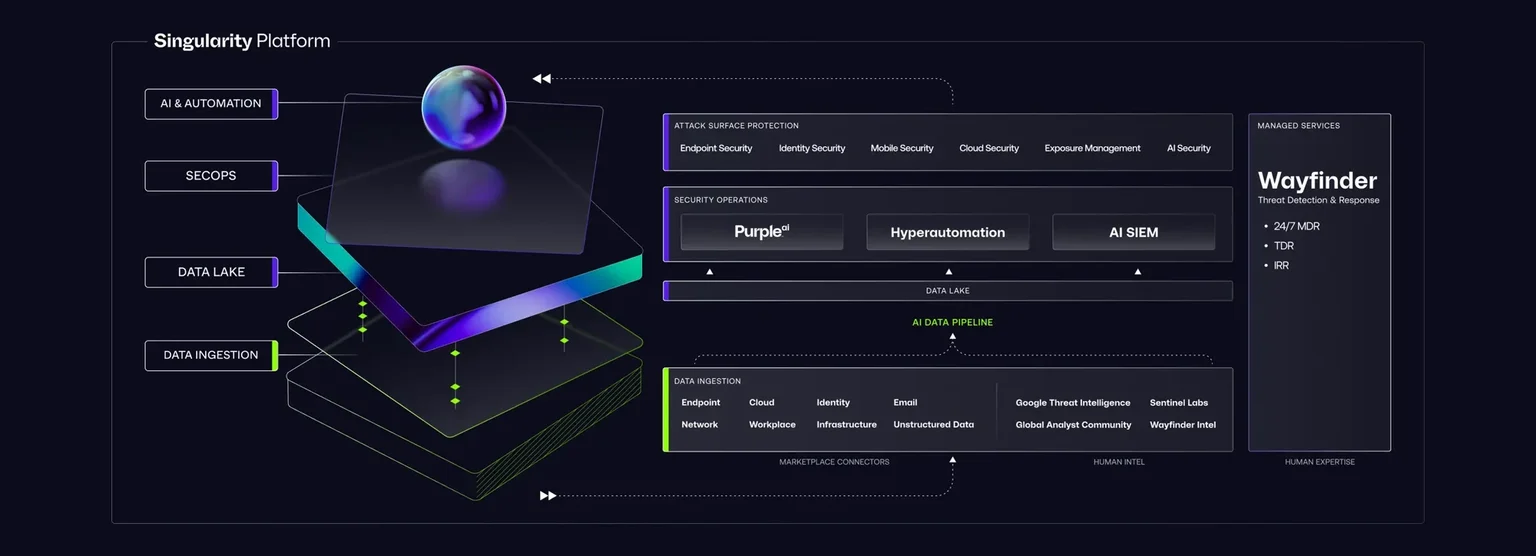
Attack surface protection, security operations with Purple AI, Hyperautomation and AI SIEM, and a data lake, together with Wayfinder services: MDR, TDR and IR.
Behavioral analysis of processes on endpoints and servers to block threats instantly.
Active protection for Active Directory and Entra ID, preventing lateral movement in the network.
Continuous monitoring, threat hunting and incident response around the clock by a team of analysts.
Mapping of AI applications, real-time enforcement of security policy and prevention of data leakage.
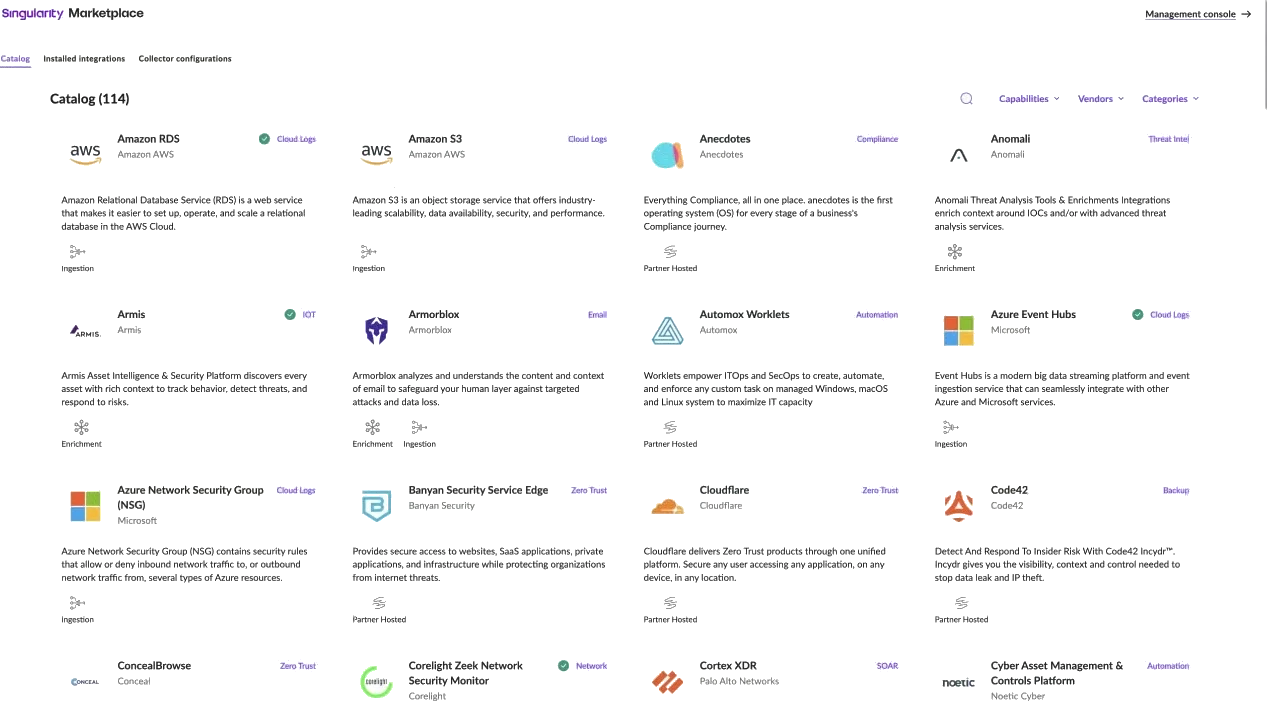
A catalog of 114 integrations for cloud, identity, Zero Trust, backup, email and SOAR, which connect the organization's data to the platform.
Analyzing the organization's computing and identity infrastructure and defining security requirements.
Defining the deployment architecture, the enforcement policy and the integration processes for the environment.
Installing agents, connecting to Active Directory and deploying the containment mechanisms.
Ongoing engineering support, periodic reviews and incident management together with the SOC team.
Stopping privilege escalation attempts and lateral movement in the network with deception mechanisms.
Identifying unapproved Shadow AI applications and preventing the transfer of sensitive data.
Real-time detection and blocking of unknown attacks, with no dependence on signature updates.
A view of threats and endpoints, and the Purple AI verdict on an alert, in one console.
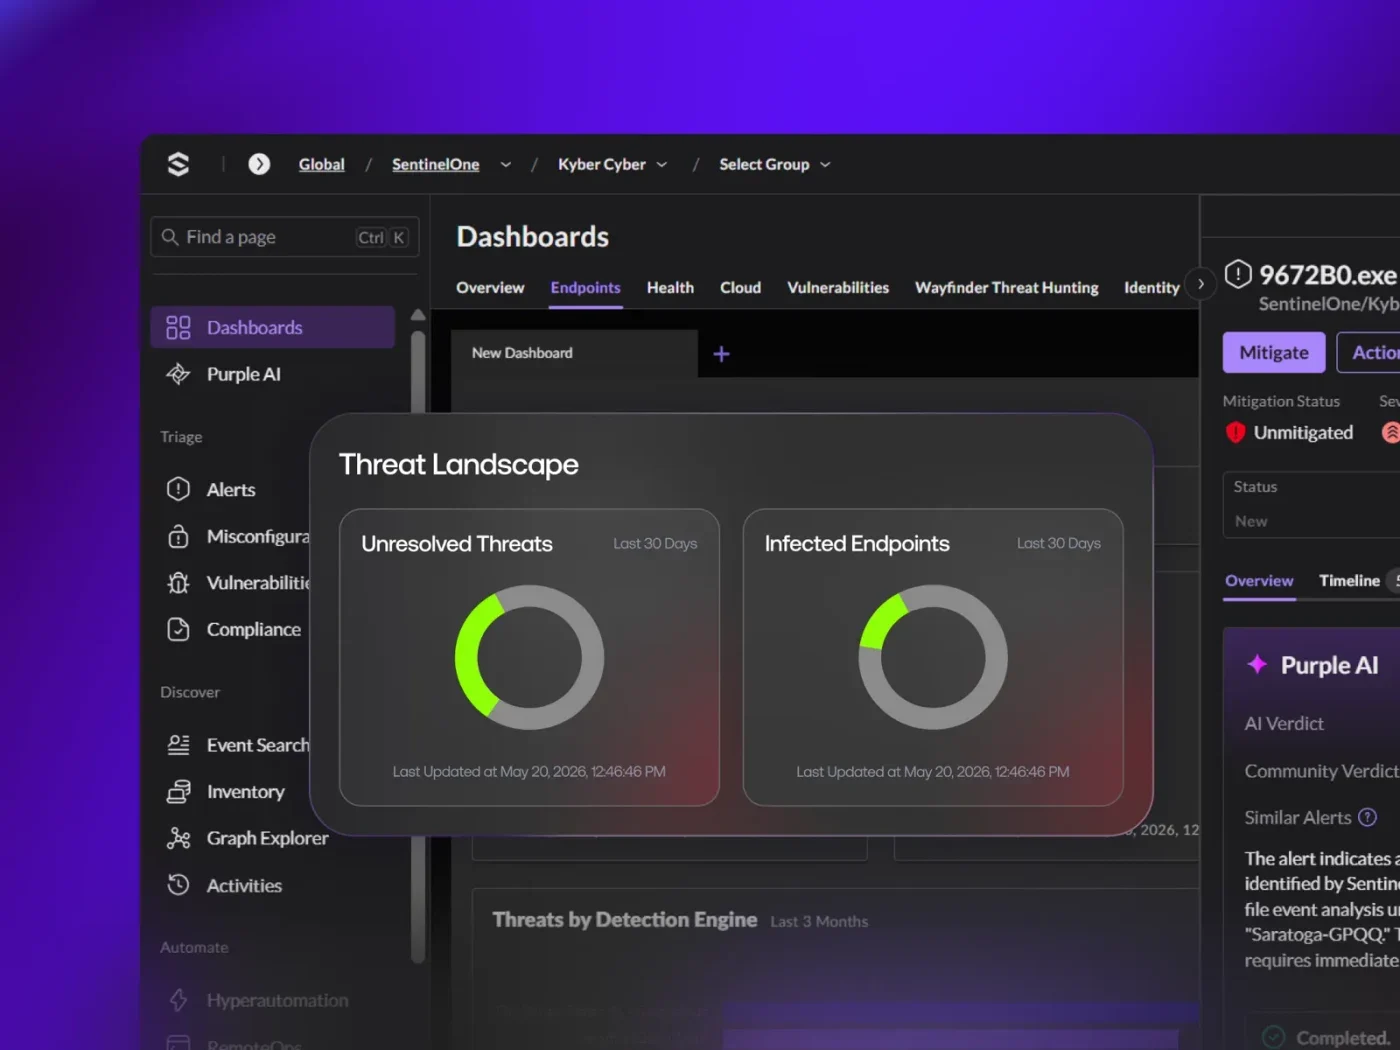
SentinelOne runs dynamic monitoring engines that analyze process behavior in real time on the endpoint, and it identifies malicious patterns of activity even without prior knowledge of the code.
The Identity component monitors privilege escalation attempts and malicious policy changes in AD and Entra ID, and disrupts the attack vector with deception using Hologram decoys and fake data.
The service provides 24/7 monitoring that combines AI with a human analyst team, proactive Threat Hunting, investigation based on XDR data, attack containment and recommendations for hardening the environment.
Prompt Security identifies and maps GenAI applications and Shadow AI components, logs interactions, assesses risk and enforces data loss prevention (DLP) policy in real time.
DnA IT provides Turn-Key integration services, from the architecture discovery stage and defining the enforcement policy, through integration with the organization's systems, to ongoing engineering support in Hebrew.
We'd be glad to review with you which parts of your information systems are ready for an upgrade, and to propose technology solutions backed by decades of hands-on field experience.
Book a meeting